Authorize components
Before you install any on-premises component (Broker, Workstation Agent, Directory Synchronization Agent (DSA), SaaS Agent, or OpenLM Router), you must generate an authorization file for it. AI Proxy is the exception: it connects with a client ID and secret, as described in AI Proxy. The authorization file is a credentials file that contains a client ID and secret, confirming the component is trusted and allowed to connect to OpenLM Platform.
Generate one authorization file per component type before you begin installation. A single Workstation Agent file can be shared across many agent machines, while Broker and DSA are typically authorized individually.
Generate an authorization file
To generate an authorization file:
-
Open Navigation (the grid icon in the header).
-
Select Platform Administration, then Identity.
-
Select the Authorization tab.
-
Select Add Client.
-
Select the client type:
- Broker: for an OpenLM Broker.
- Agent: for a Workstation Agent.
- Dsa: for a Directory Synchronization Agent.
- SaaSAgent: for a SaaS Agent. See Connect the agent to OpenLM.
- Router: for an OpenLM Router. Leave Encrypted authorization client cleared. See Get the Router authorization file.
-
Enter a description (required).
The following screenshot shows the form with Broker selected and a description entered.
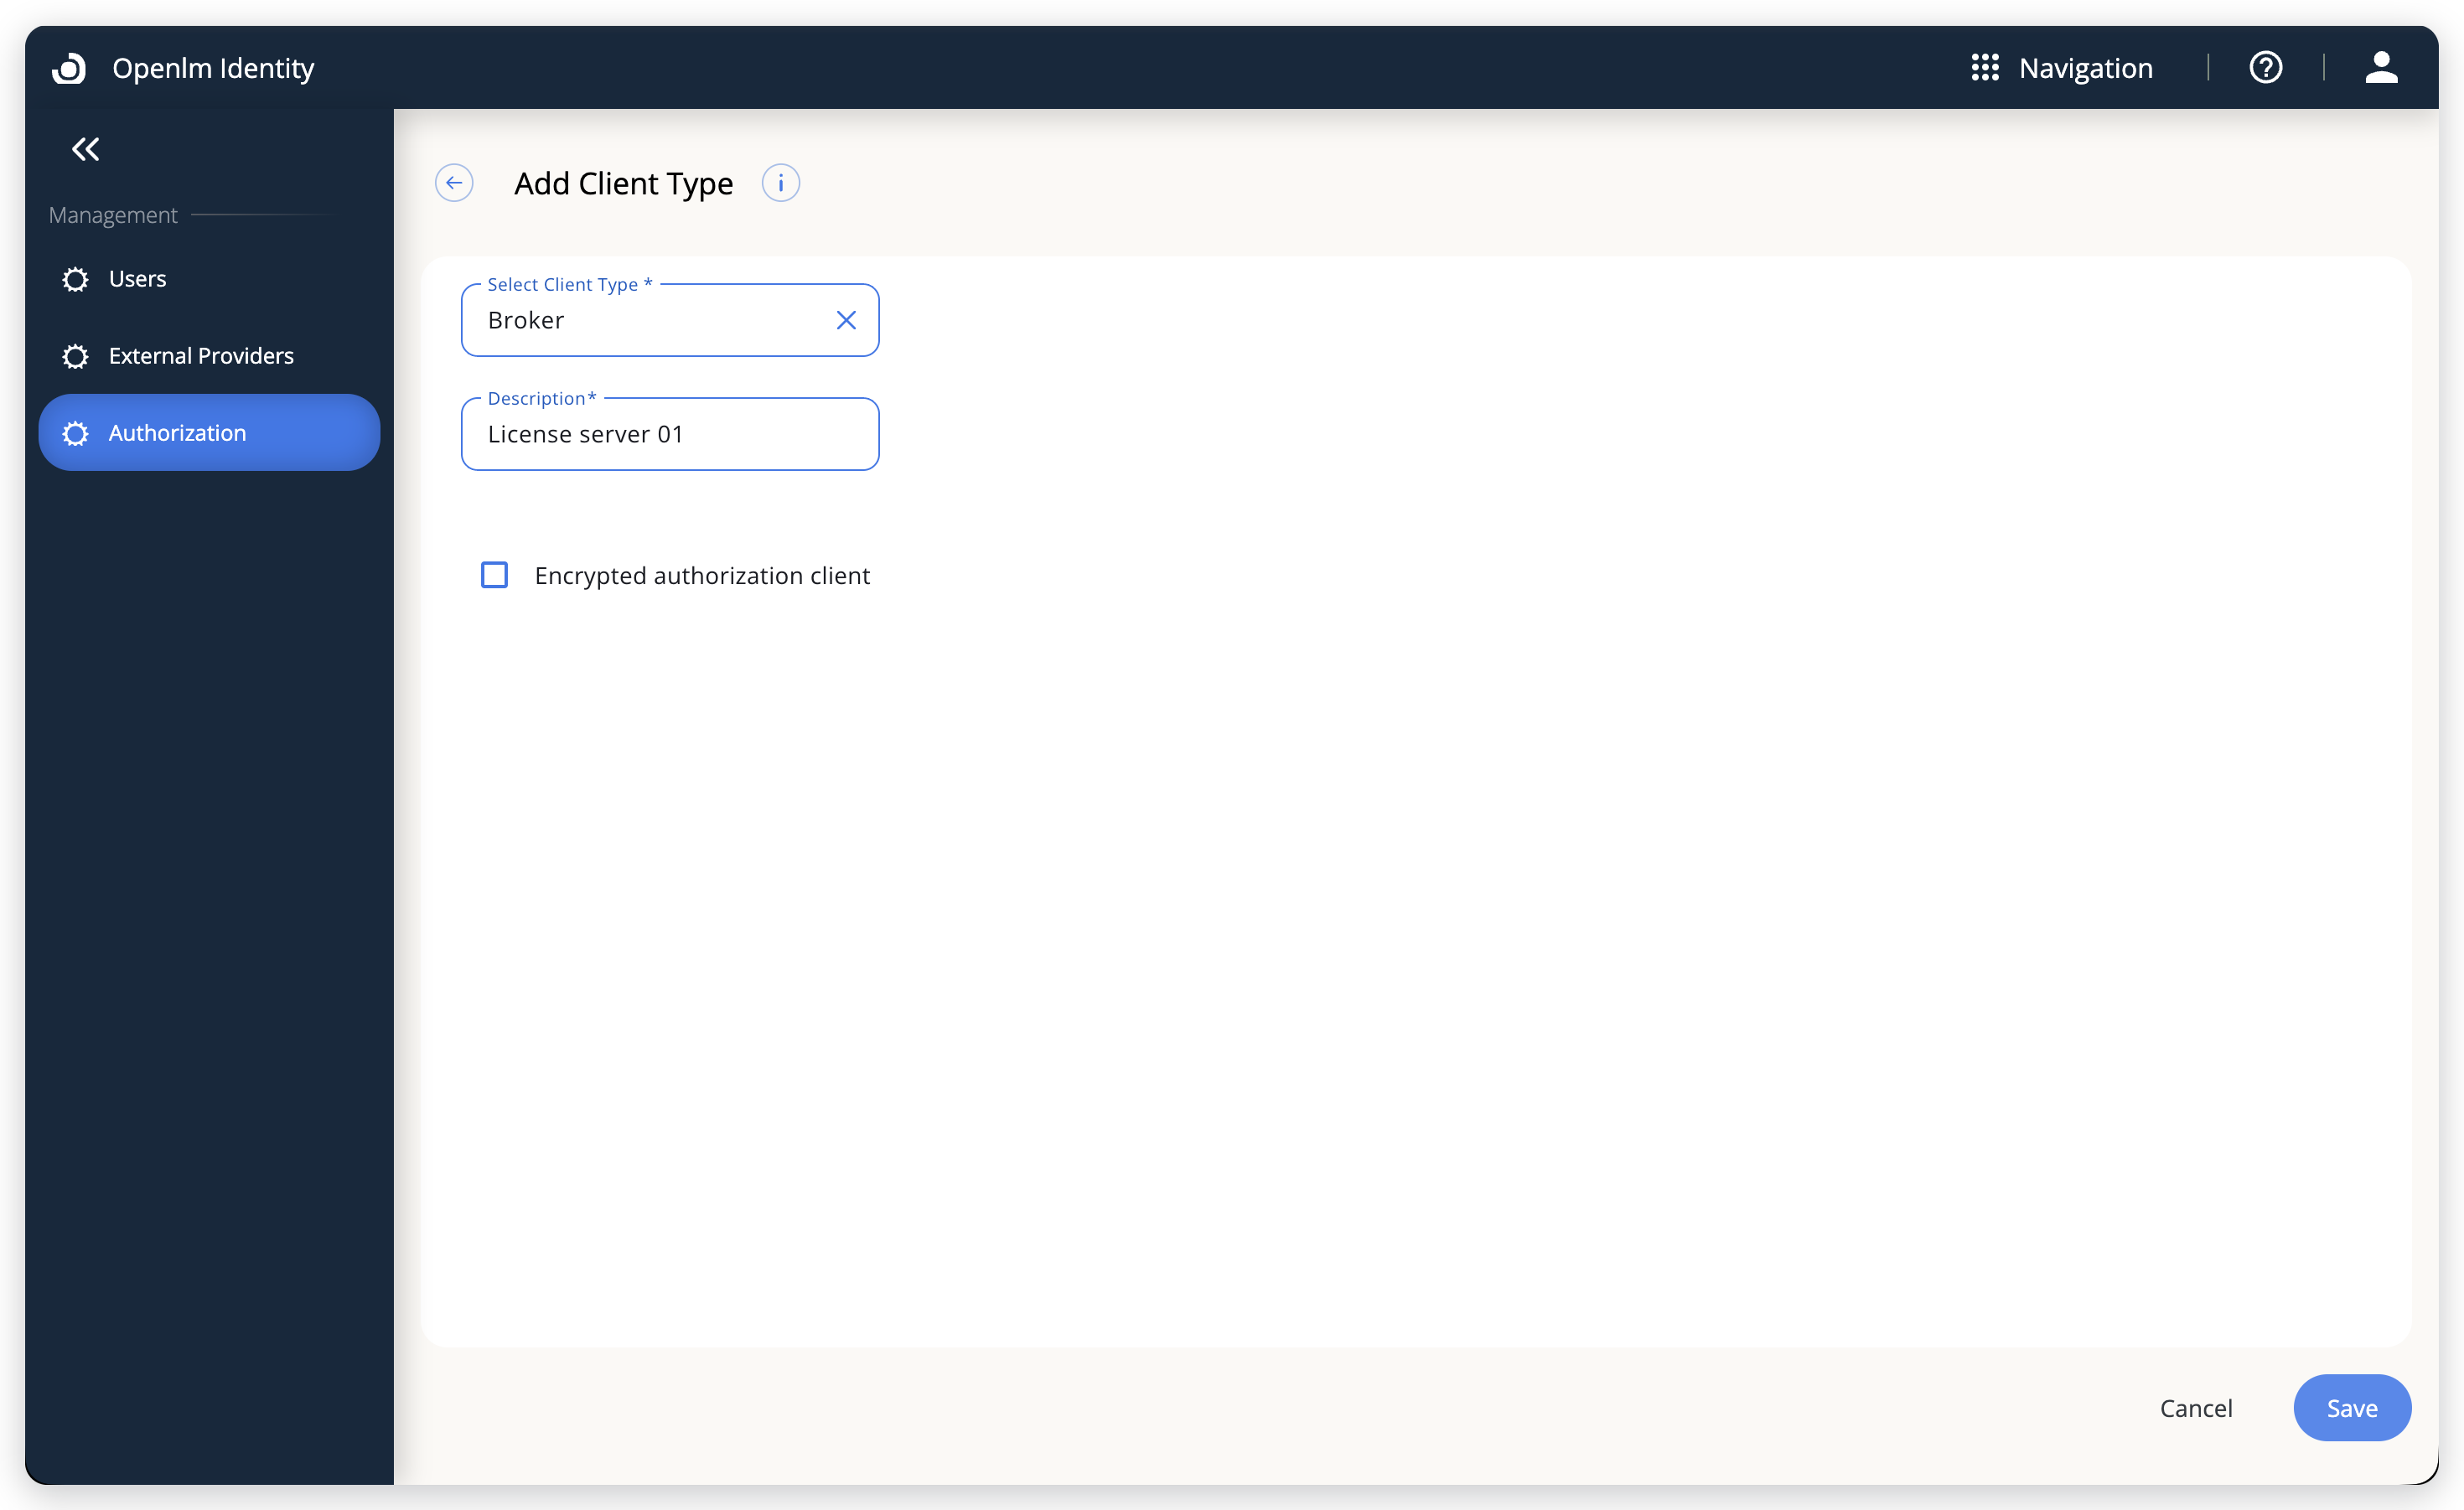
Adding a Broker client in the Authorization tab of Identity.
-
(Optional) Select Encrypted authorization client to generate an encrypted credentials file. Don't select it for a Dsa client or a Router client: the DSA installer accepts only the plain
dsa-authorization.jsonfile, and the Router needs the plain file. -
Select Save.
-
In the Secret Key dialog, copy the Client ID and Secret Key, or select Download to save the entire file as
.json.For an encrypted client, copy or download the Encrypted Client text instead.
The following screenshot shows the generated Client ID and Secret Key.
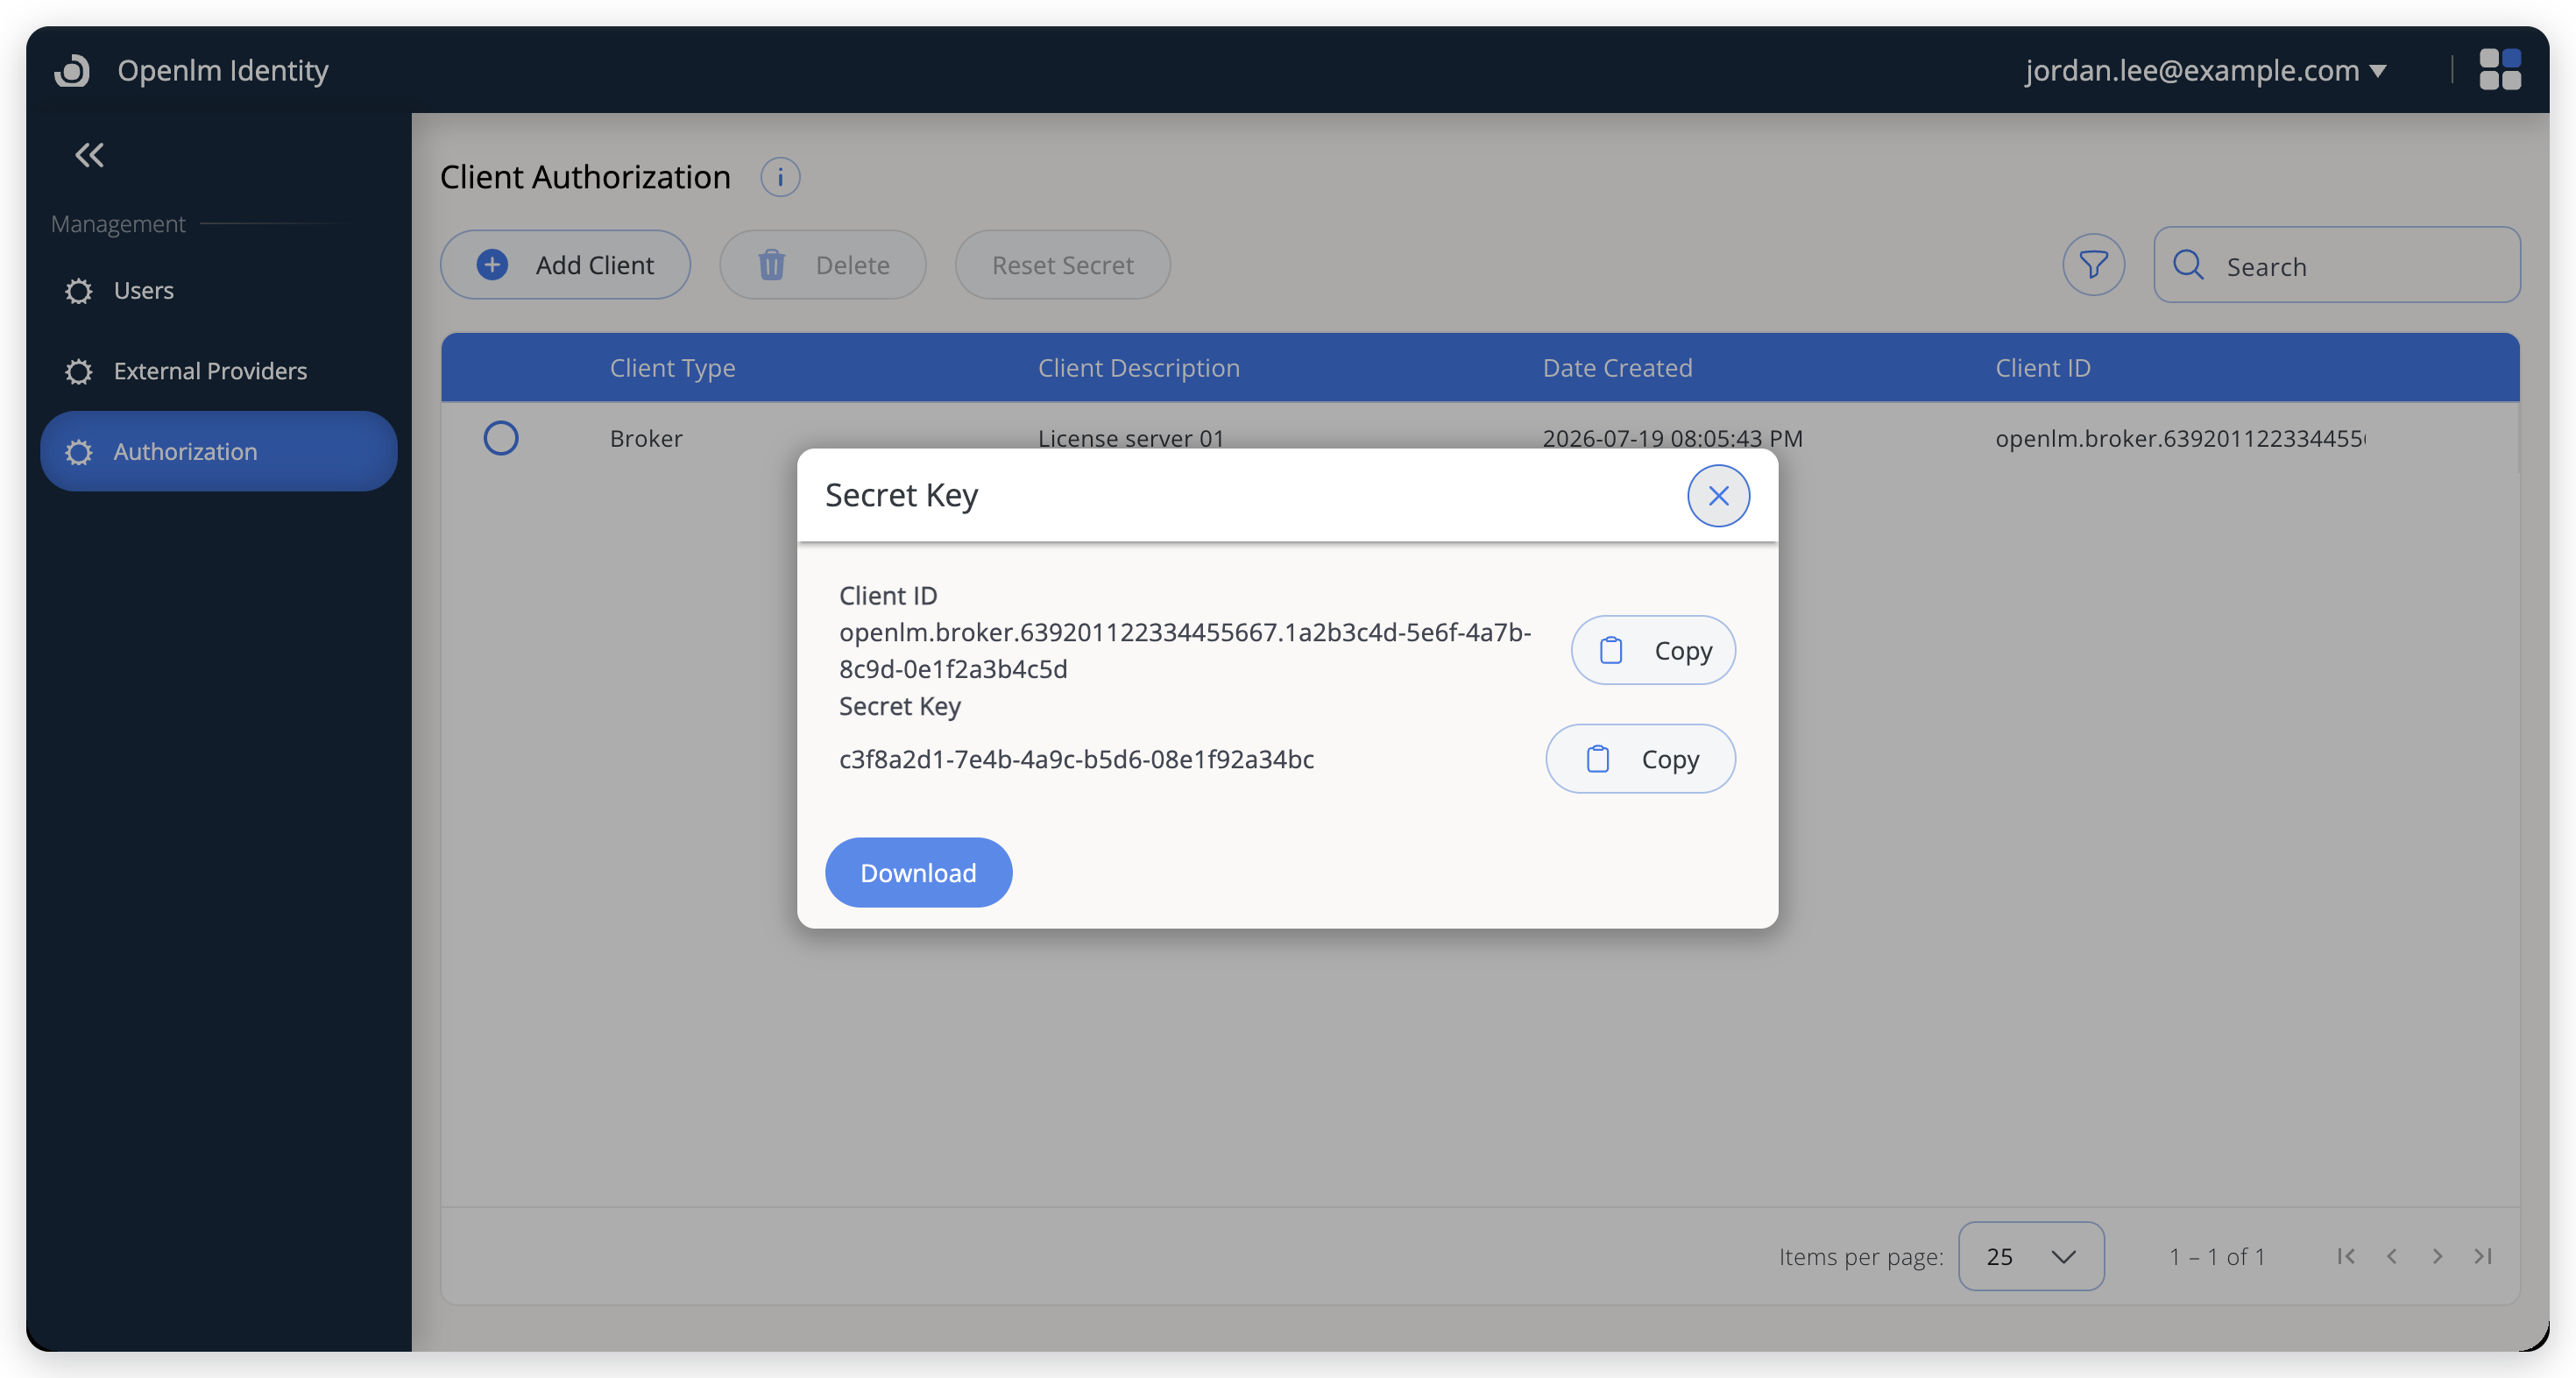
The generated Client ID and Secret Key.
Keep the downloaded .json file accessible. You import it during each component's installation.
AI Proxy
AI Proxy doesn't use an authorization file. On an OpenLM Platform that is secured, an administrator who manages Identity creates a Client ID and Client Secret for it, and you enter them in the AI Proxy UI with the Location of your OpenLM Platform. See Configure AI Proxy.
If you delete an authorization entry later, components using it immediately lose access to the system. To rotate a client secret, select the entry and select Reset Secret, then download the new file. The previous secret becomes invalid.
For full details on Identity service configuration, including single sign-on (SSO), role-based access control (RBAC), and user management, see Identity.
Continue to Install the components to install the Broker, the Workstation Agent, and the DSA.
The documentation team might draft this page using a large language model. A technical writer reviews every page and verifies it against the product before publishing it. A human makes the final decision.