Identity
Use Identity to manage OpenLM Platform users, configure single sign-on (SSO) with external providers, and generate authorization files for OpenLM components.
To open Identity, select Navigation (the grid icon in the OpenLM Platform header), then Platform Administration, then Identity. For related tasks, see OpenLM Products.
Identity is always active for your account because it is a core system product.
Authentication and SSO
You can connect to external identity providers for authentication. Supported options include Okta, Azure Active Directory, and OpenID Connect.
Role-based access control (RBAC)
Identity defines the following roles to control access:
- Administrator: Full system access, including configuration and management.
- Viewer: Read-only access to data and reports.
For Software License Management, the Products and Roles tab also offers an Admin and a Viewer role for each of its services, so you can give a user one service without the others. The product's own Admin and Viewer roles still give access to all of them.
The following table lists the roles for each service and what they give access to:
| Role | Gives access to |
|---|---|
| Licenses Admin, Licenses Viewer | The Licenses service only. The Admin role can also change how licenses are counted or displayed. |
| License Servers Admin, License Servers Viewer | The License Servers service only. The Admin role can also approve, deny, edit, and delete servers. |
| Denials Admin, Denials Viewer | The Denials service only. The Admin role can also select which denials are recorded or excluded. |
For more information, see Licenses, License Servers, and Denials.
When a user has more than one of these roles, each app gets the highest access any of them gives. For example, Viewer together with Licenses Admin gives admin access to Licenses and read-only access to the other Software License Management apps.
Data retention
OpenLM Platform retains user data for the duration of the subscription. When a subscription ends, OpenLM deletes data in accordance with the service agreement:
- Active subscription: Full data retention.
- Suspended account: Data retained for 30 days.
- Deleted account: Data removed after 60 days.
Manage users
To add, edit, or delete a user, open the Users panel. Account administrators can add users and edit or delete existing users. The user who creates a cloud account automatically receives an Account Administrator role.
Users on this panel are sign-in accounts: people who sign in to OpenLM Platform. A person whose license usage OpenLM monitors but who never signs in is a monitored user, managed in Users and Groups.
Add a user
To add a user:
-
In the Users tab, select Add User.
The following image shows the Users page in Identity:
 Users page in Identity
-
In the General tab, enter the user's email address.
The user receives sign-in details and a link to OpenLM Platform at this email address.
-
(Optional) To create an inactive user, turn off the Status toggle. It is on by default.
-
(Optional) Enter a first name and a last name in First Name and Last Name.
Users or account administrators can update these fields later.
-
Set a temporary password.
-
(Optional) Select User must change password at next login.
-
If the user needs to manage other users, turn on the Account Administrator toggle.
The following image shows the Add User dialog:
 Add User dialog in Identity
-
In the Products and Roles tab, set the user's access level (Admin or Viewer) for each activated product.
The following image shows the Products and Roles tab with the Alerts drop-down list open:
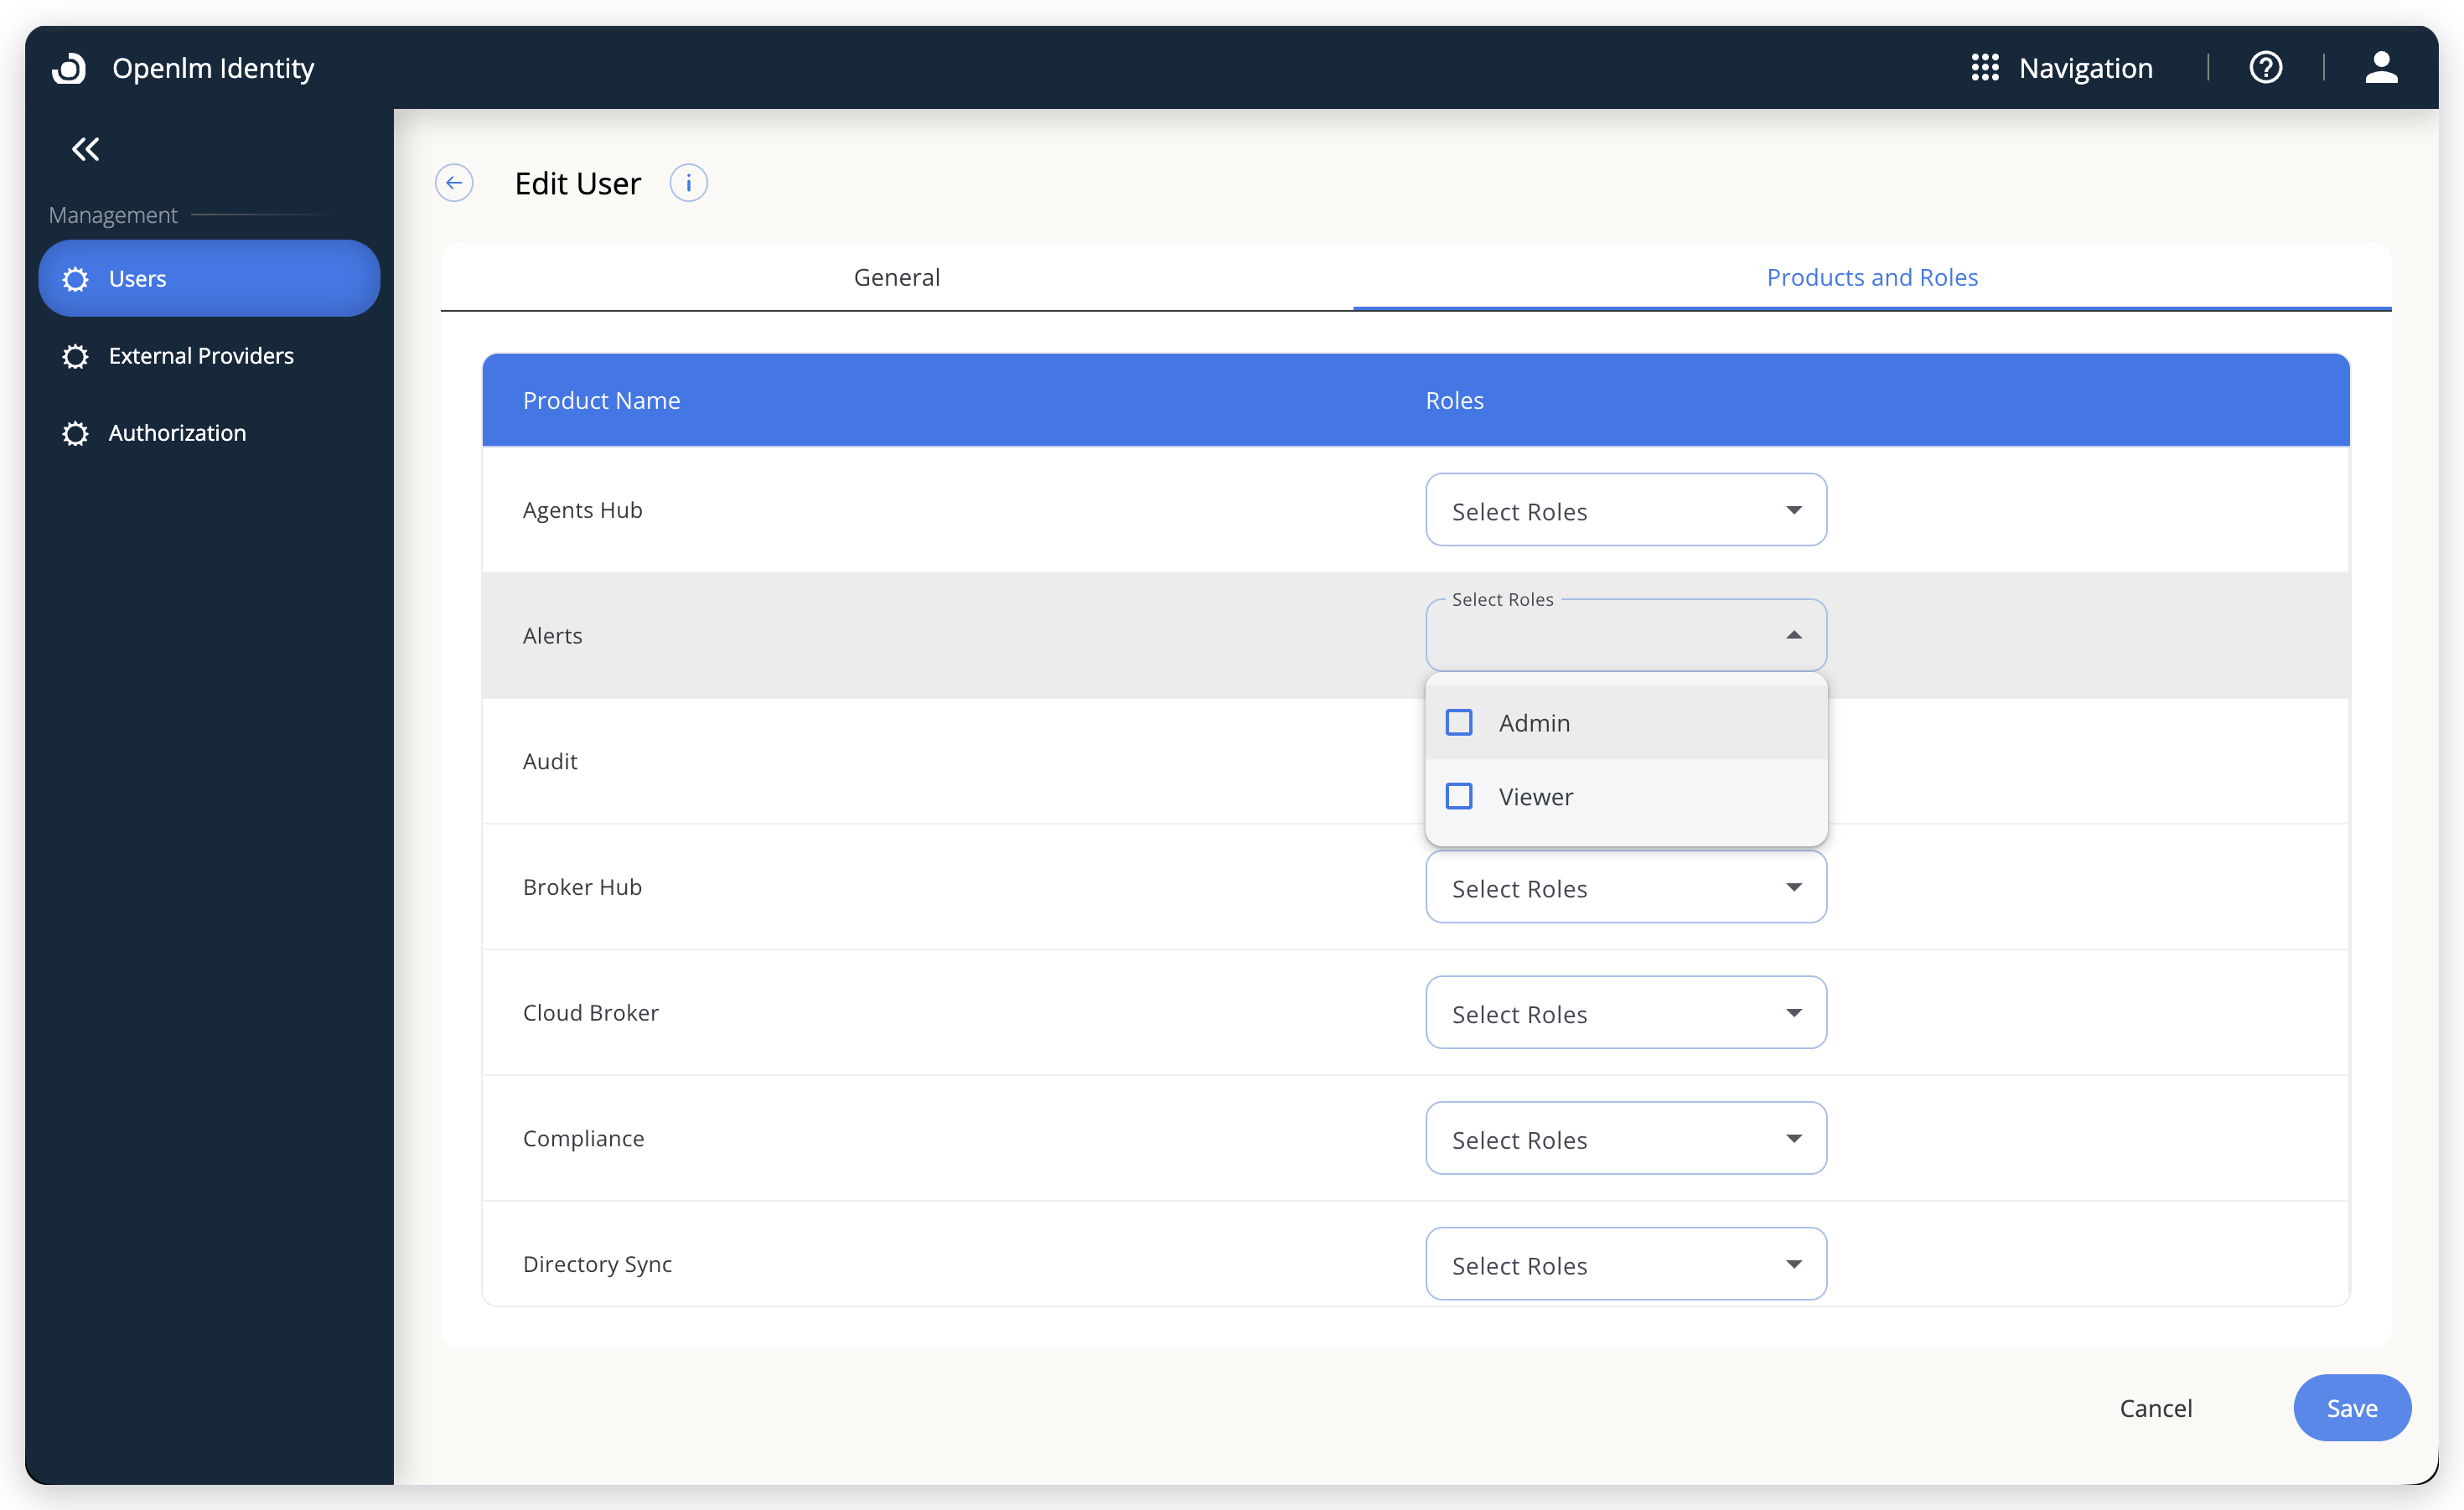 Products and Roles configuration in Identity
-
Select Save to confirm your settings.
For Software License Management, you can also give access to a single service. For more information, see Role-based access control (RBAC).
You can also watch the interactive guide for adding a user and assigning roles:
Interactive guide - expand to see
Delete a user
To delete one or more users:
-
Select the users you want to delete.
-
Select Delete.
-
Confirm your action when prompted.
To temporarily deactivate confirmation prompts, select Don't ask for next 5 minutes.
Edit a user
To edit user details:
- Hover over the user's row.
- Select the Edit (pencil) icon.
- Change the user details.
- Select Save.
External providers (SSO)
Use the External Providers tab to configure SSO with identity providers such as Okta, Active Directory Federation Services (ADFS), Azure, or OpenID Connect (OIDC).
Add an SSO provider
To add an SSO provider:
-
Select Add Provider.
The following image shows the Add External Provider step:
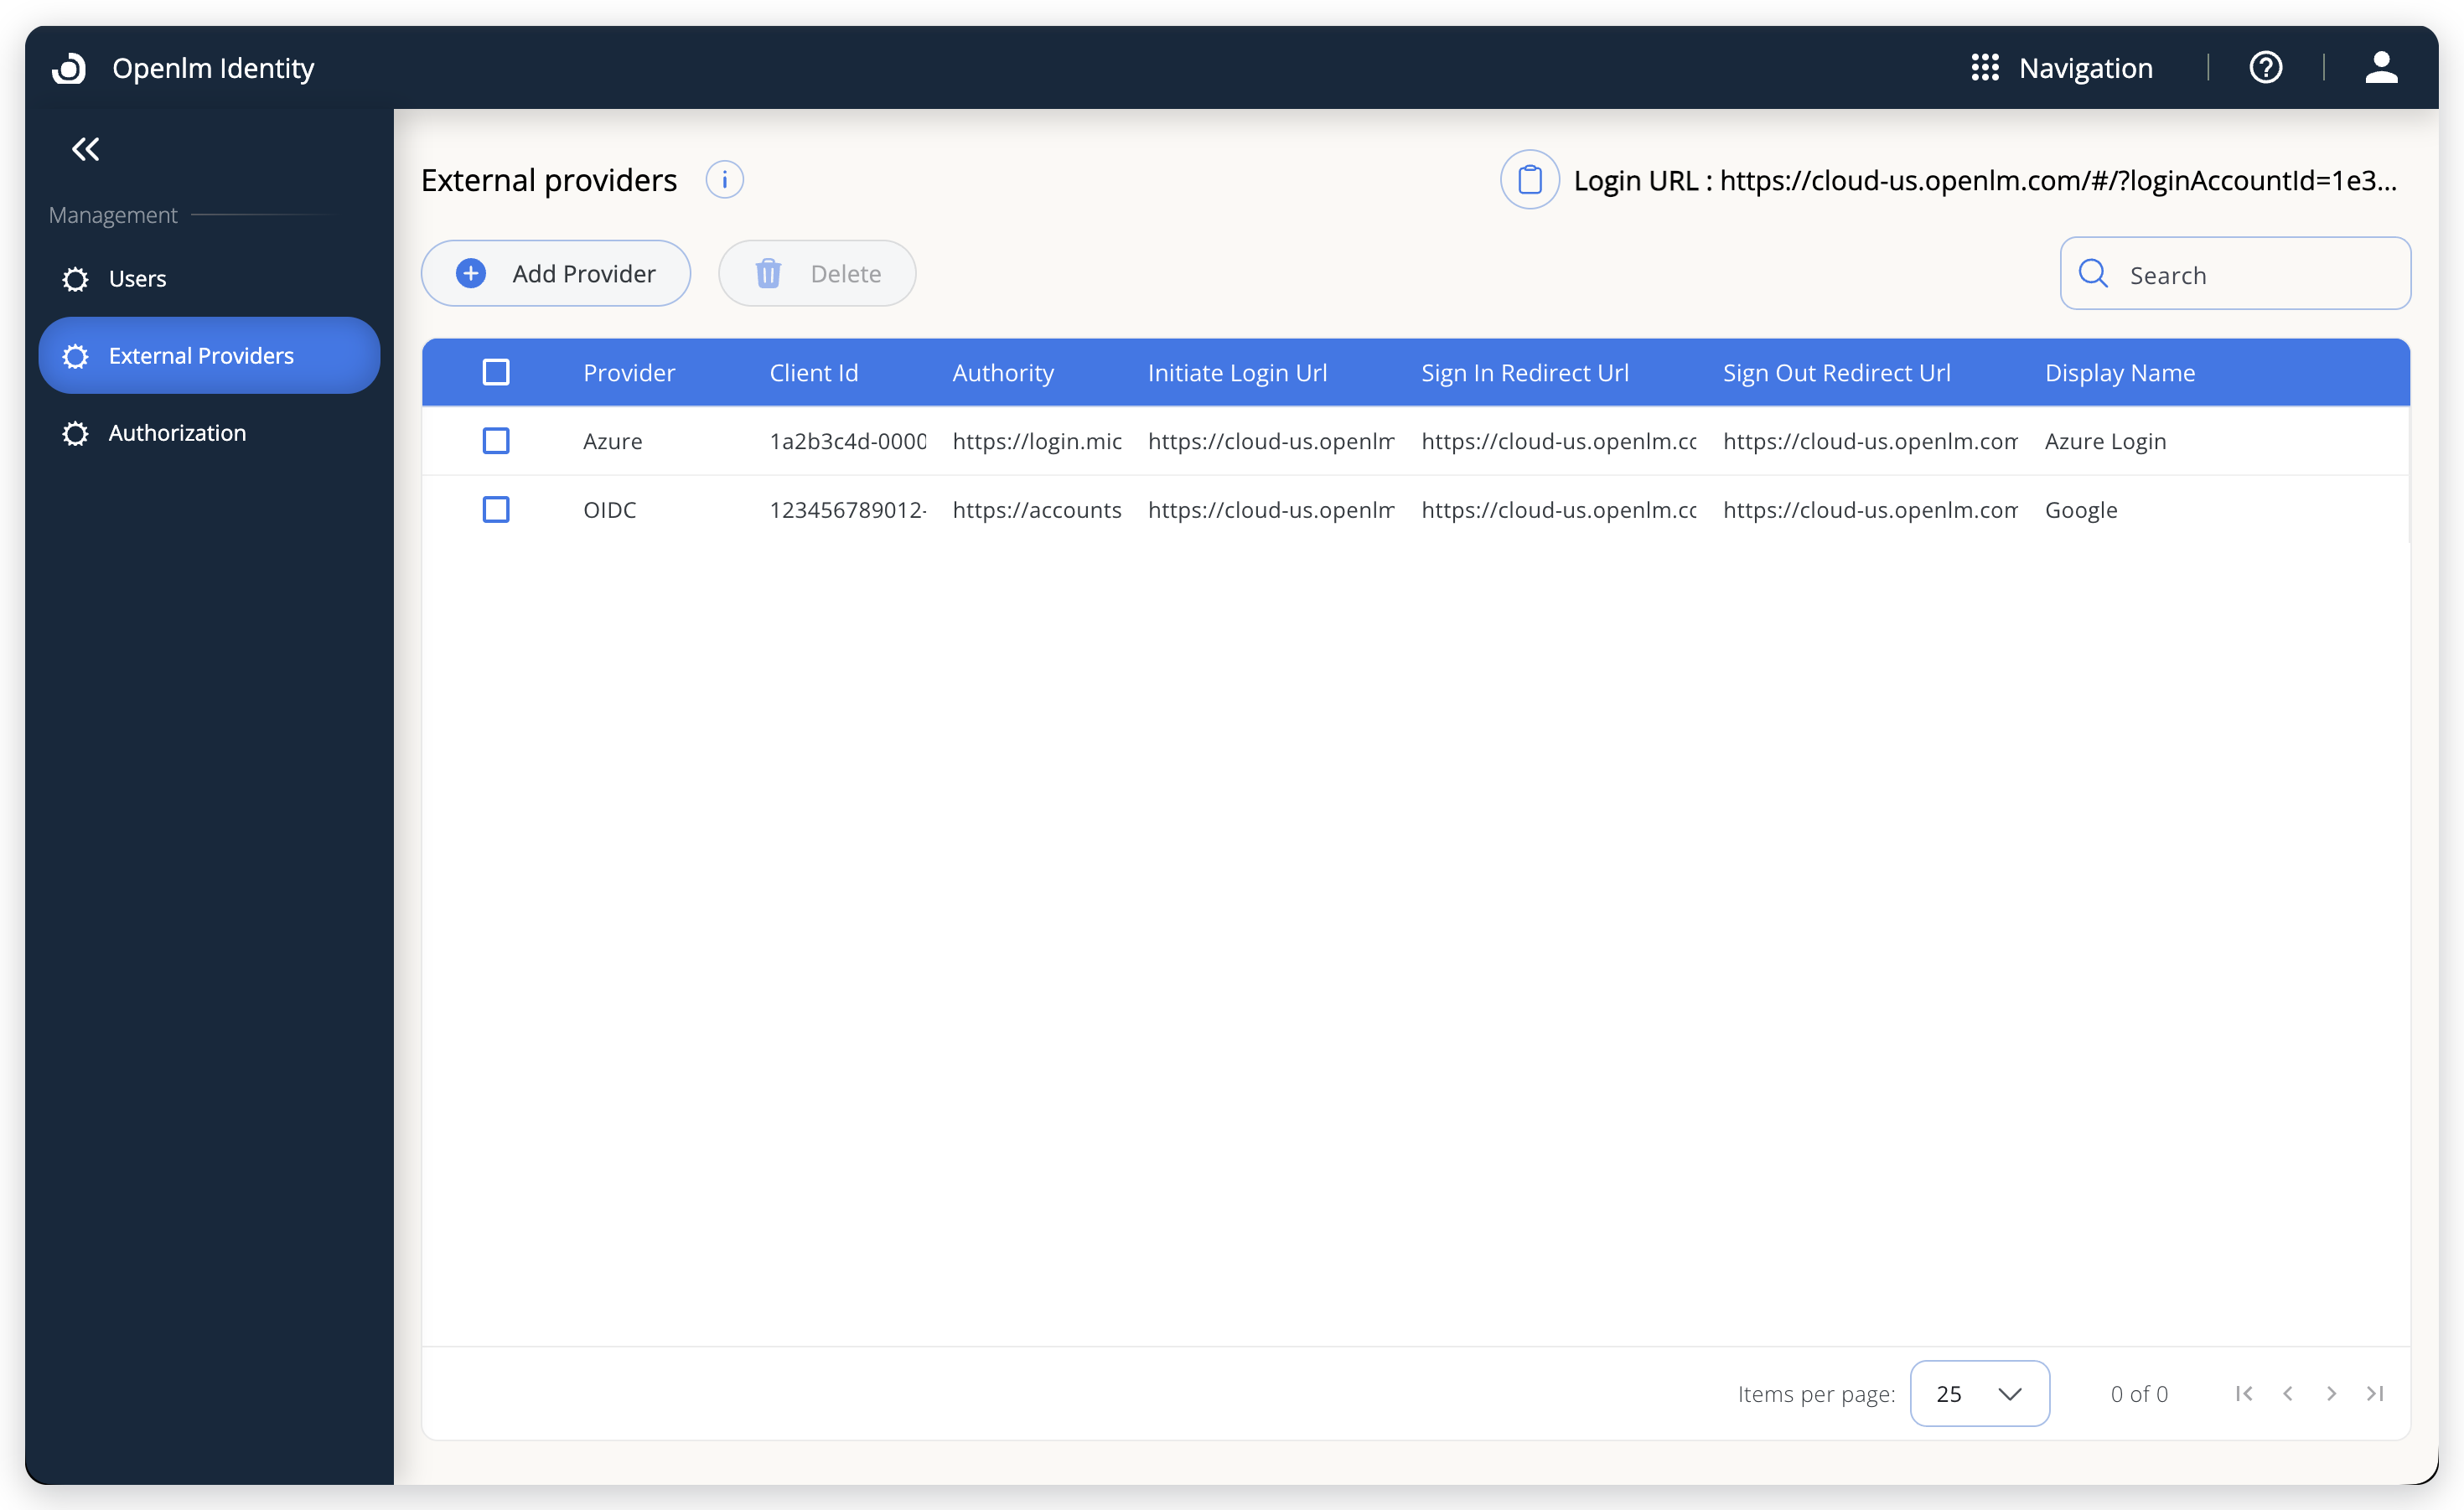 Add External Provider step in Identity
-
From the drop-down list, select one of the following providers: Okta, ADFS, Azure, or OIDC.
-
Enter the required details from your provider account:
- Client ID
- Client Secret
- Authority (for example,
dev-12345678.okta.com) - Display Name
Delete an SSO provider
To delete an existing SSO configuration:
- Select the provider you want to delete.
- Select Delete and confirm the action when prompted.
To sign in through SSO, access the system using the link generated as Login URL along with your account ID.
Client acting
The Client Acting setting determines how OpenLM Identity communicates with your Identity Provider during SSO authentication. Select one of the following options:
- Authorization Code Flow (Secure - Recommended): Use this option when your Identity Provider requires secure token handling and does not allow implicit grants. With this option, you authenticate using an authorization code, which offers improved security and support for refresh tokens.
- Implicit Flow (Basic): Use this option only if your Identity Provider allows it. Tokens are passed directly through the browser.
Check with your IT or security team to confirm which method your Identity Provider supports before you configure this setting.
The following image shows the Add External Provider dialog:
 Add External Provider dialog in Identity
Authorization
To let OpenLM components authenticate with Identity, generate authorization files in the Authorization tab. Components without valid files are denied access.
Generate an authorization file
To generate an authorization file:
-
Select Add Client.
-
Select the client type.
-
(Optional) Add a description.
-
Select Save.
-
Copy and paste the provided client ID and secret, or download the entire file as
.json.The following image shows the generation of an authorization file:
 Generating an authorization file
Delete an authorization file
Deleting an authorization file affects the components that use it.
After you delete an authorization file, components that use it lose access to the system.
To delete an existing authorization file:
- Select the authorization entry.
- Select Delete and confirm the action when prompted.
Reset client secret
Resetting a client secret affects the components that use it.
After you reset a secret, the previous secret becomes invalid, and components that use it no longer connect to the system.
To reset a client secret:
- Select Reset Secret on the authorization entry you want.
- Confirm the action in the confirmation window.
- Copy the new secret or download the new authorization file.
The documentation team might draft this page using a large language model. A technical writer reviews every page and verifies it against the product before publishing it. A human makes the final decision.