Keycloak integration with OpenLM
Keycloak configuration
Prerequisites
- Keycloak MUST run HTTPS
- No spaces allowed in usernames
Configuration
-
To get the authentication configuration for Keycloak, open:
<keycloakURL>/realms/<realm-name>/.well-known/openid-configuration
Replace<keycloakURL>with the URL of your Keycloak server and<realm-name>with your realm name. For example, for themasterrealm:
http://localhost:8080/realms/master/.well-known/openid-configuration -
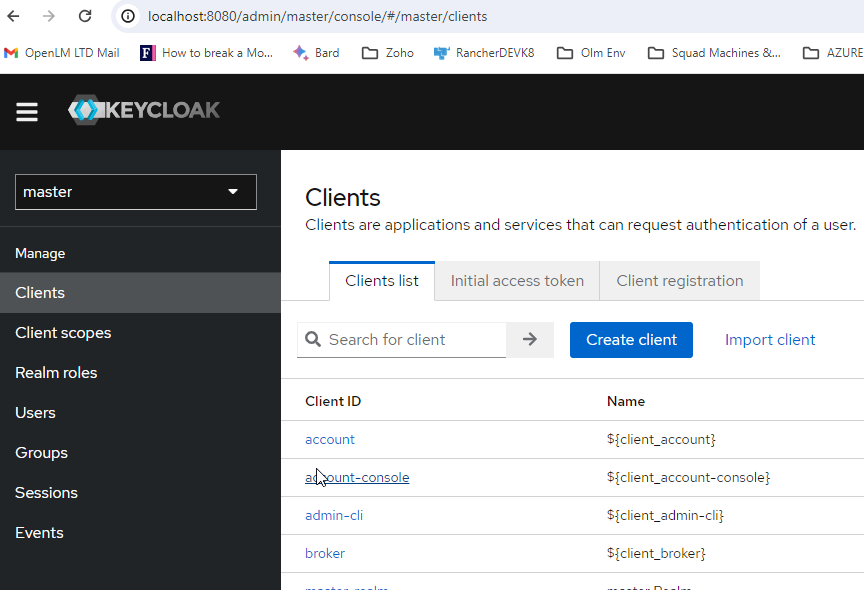
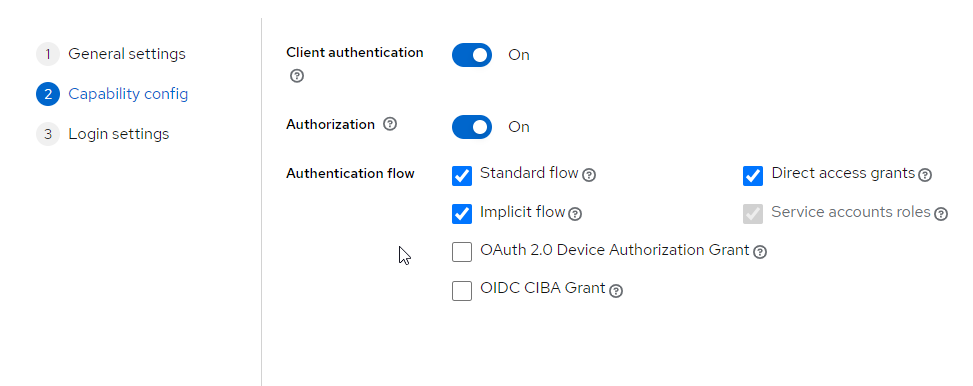
To define a client, log in to the administration console, select Clients tab in left menu, then select Create Client button:
-
Save the client.
-
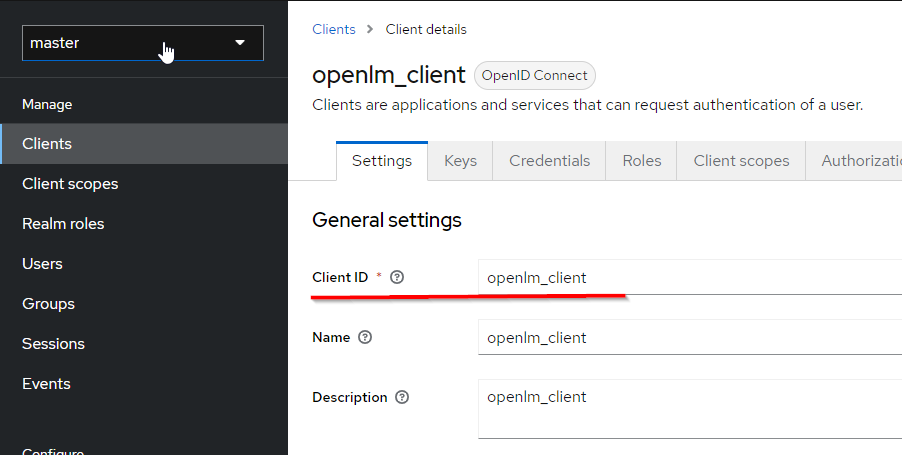
Select the client to see its details.
-
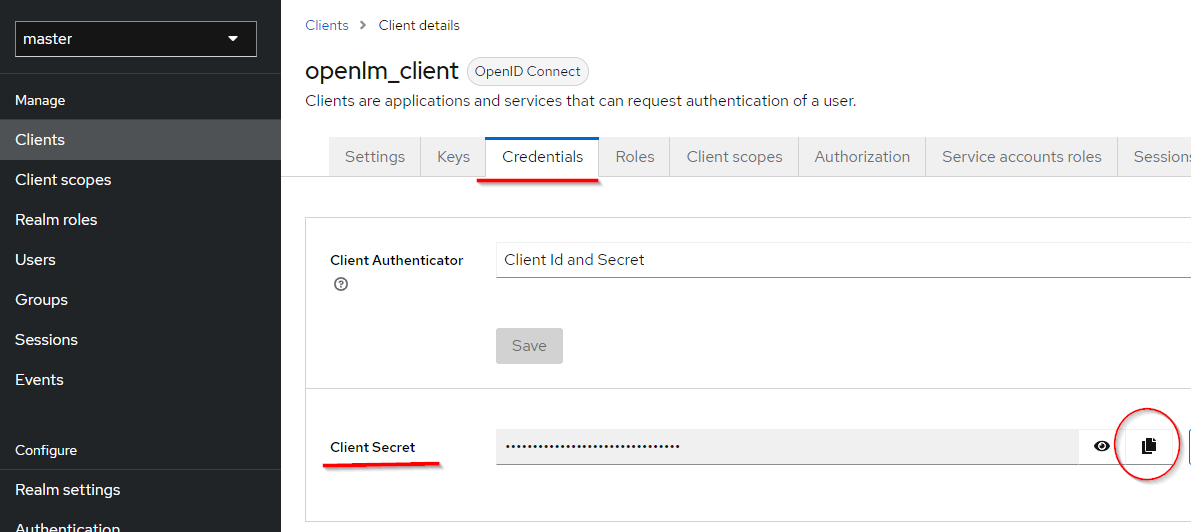
Add an OIDC external provider in the Identity Service or the Cloud Portal, and use the following Client ID and Client Secret:
-
Authority should be filled with the issuer value from the configuration returned in step 1.
Note - in some cases one needs to usekeycloak-url/auth/realms/master/.well-known/openid-configuration
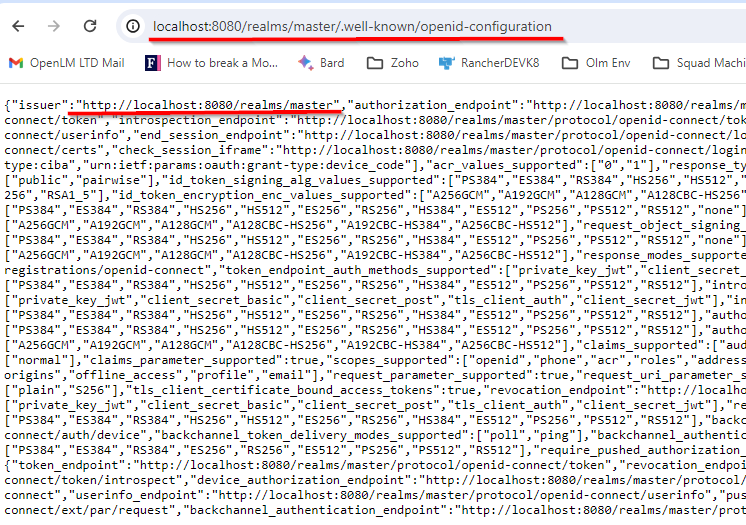
-
Save the external provider.
-
Edit the Keycloak client and add the redirect URI from the OIDC external provider config in Identity Service:
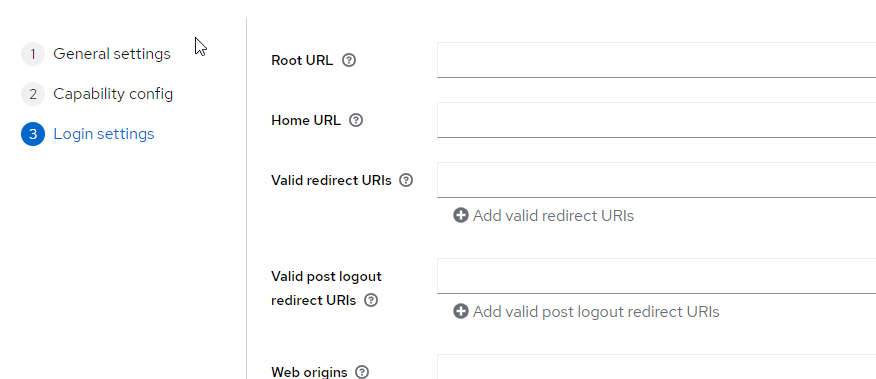
-
Save the client.
The documentation team might draft this page using a large language model. A technical writer reviews every page and verifies it against the product before publishing it. A human makes the final decision.