
Ask five people in your organization to define software compliance, and you’ll likely get five different answers. Some will describe it as “not getting sued.” Others will call it an IT problem, a procurement issue, or something the legal team handles once a year during renewal season.
All of them are partly right, and that’s exactly why compliance gaps keep showing up in audits.
Here’s a working definition you can build a policy around: software compliance is the practice of using the application strictly within the terms of its license agreement, including seat counts, deployment scope, user roles, and permitted use cases. It’s a contractual obligation, not a best practice. When you’re out of compliance, you’re in breach of an agreement, and vendors have gotten far more sophisticated about catching that.
What is software compliance: How is it distinct from software optimization?
You’ll often see these two terms used interchangeably, and that’s where a lot of confusion starts. Think of it like the difference between staying within the speed limit and choosing the most efficient route. Compliance keeps you within the boundaries your license agreement sets. Optimization is about getting the most value out of what you’re already allowed to use.
Compliance asks: are you deploying this software the way your contract says you can?
Optimization asks: are your license counts, tiers, and usage patterns actually matched to how your teams work?
You can be fully compliant and still badly optimized, paying for far more seats than anyone touches. You can also be optimized on paper and still non-compliant, running a floating license pool that regularly exceeds its entitlement during peak deadlines.
The two goals reinforce each other, though. A team that tracks usage closely to optimize spend usually catches compliance drift as a side effect, because both depend on the same underlying data: who’s using what, how often, and under which terms.
Additional Read: Enterprise software license management: A buyer’s guide for IT and engineering leaders
Why compliance deserves its own focus right now
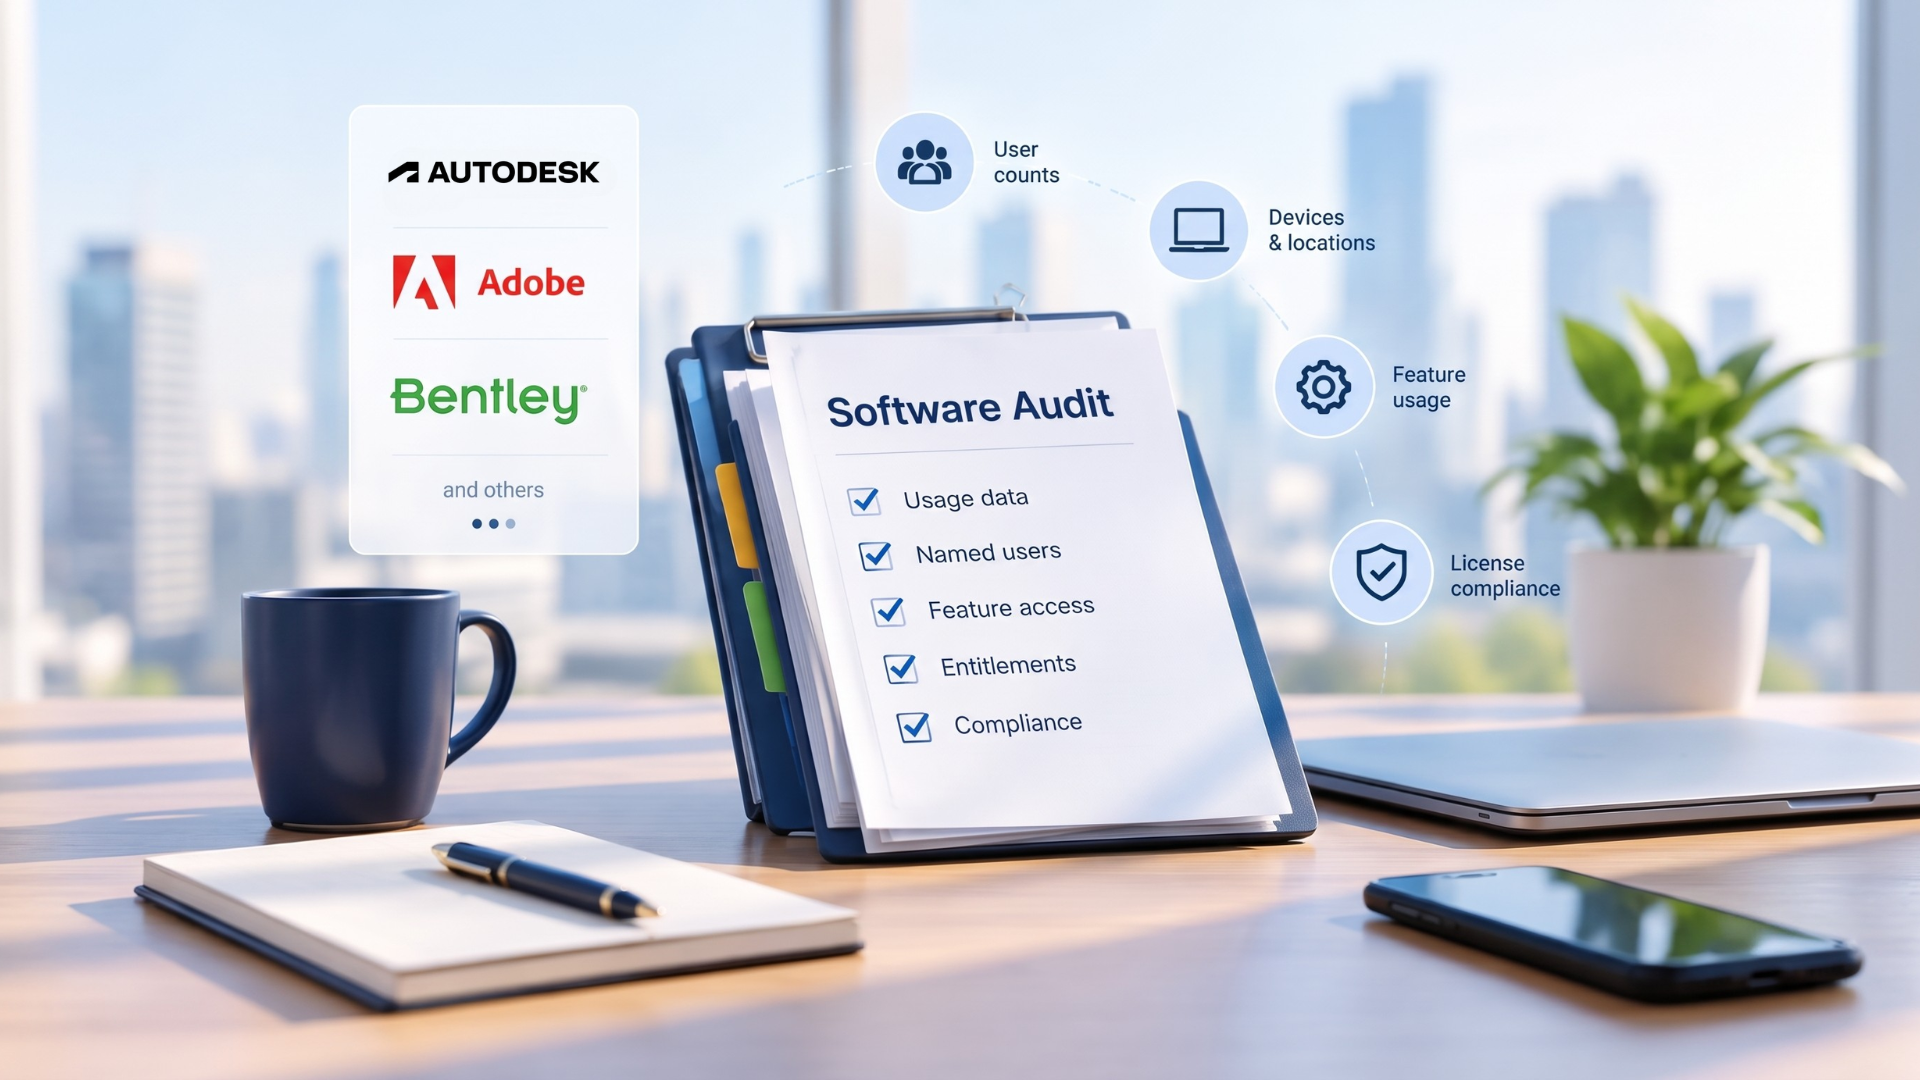
Vendor audits aren’t rare events anymore. Major publishers in engineering and design software run compliance checks as a standard part of their revenue operations, and the stakes go up as licensing models shift toward usage-based and subscription structures that are easier to instrument and easier to verify. If your organization runs high-cost specialty tools from vendors like Autodesk, Bentley, or Esri, you’re a more attractive audit target simply because the per-seat cost of a compliance gap is higher.
There’s also a security dimension worth naming as October’s Cybersecurity Awareness Month approaches. Unmanaged or unauthorized software installations create licensing risk, and they widen your attack surface too. Shadow deployments of engineering tools often bypass the patch management and access controls your security team has built for sanctioned software. A compliance program that tracks what’s installed, where, and by whom does double duty: it protects your budget and it shrinks the number of untracked applications a security review has to account for.
What a software compliance policy should include
A written policy turns compliance from a scramble you do before an audit into a process your teams follow every day. At a minimum, yours should cover the following:
- Ownership and accountability. Name who owns compliance for each software category, whether that’s a software asset manager, an IT director, or a shared responsibility between IT and procurement. Vague ownership is the most common reason policies go stale.
- A current software inventory. You can’t stay compliant with software you don’t know you have. Your policy should require a regularly updated record of installed applications, entitlements purchased, and where each license is deployed.
- Usage monitoring and reporting cadence. Define how often you’ll review usage against entitlements, and who receives that report. Monthly or quarterly reviews catch drift before it becomes an audit finding.
- Deployment and provisioning rules. Spell out who can install or request new software, and require a check against available entitlements before a new seat goes live.
- Acceptable use guidelines. Cover concurrent versus named-user licensing, geographic or entity restrictions, and any limits on subcontractor or third-party access, since these are common places where engineering teams unintentionally violate license terms.
- True-up and renewal procedures. Document how your organization handles a true-up when usage exceeds entitlement, and build a renewal timeline that gives procurement enough lead time to negotiate from a position of accurate data.
- An audit response plan. Decide in advance who responds to a vendor audit request, what data you’ll pull, and what your internal timeline looks like, so a request doesn’t turn into a scramble.
None of this needs to be complicated. A short, clearly owned policy that your teams actually read beats a fifty-page document that sits in a shared drive untouched until an audit notice arrives.
Getting started without a full audit team
Most IT and procurement teams don’t have a dedicated compliance function, and you don’t need one to make real progress. Start with an honest inventory: what software your teams run, what you’re entitled to, and where the two don’t match. That gap analysis alone usually surfaces your highest-risk areas.
From there, assign at least one person per major vendor relationship as the point of contact for entitlement questions, and set a recurring calendar reminder to check usage against contract terms. Even a quarterly check is a meaningful improvement over reviewing only at renewal. If automated usage-tracking tools are available to you, they remove most of the manual effort involved in staying current.
Additional Read: Software service level agreement 101: Read before you buy
What OpenLM brings to the table
By deploying OpenLM, IT teams can get continuous, real-time visibility into how their engineering software licenses are actually used. As a result, compliance stops being a once-a-year scramble and becomes an ongoing, data-backed process.
Wondering how this may look in reality? Consider, you used to put heart and soul into compiling spreadsheets before a vendor audit. Enter OpenLM, and you are now able to track entitlements versus usage from a single dashboard, across 100+ supported engineering license managers.
However, the compliance capabilities of OpenLM are not just limited to tracking Autodesk, Bentley, Esri or DSLS usage. With License Access Control, you can also set rules for who can check out a license, when, and under what conditions, so that OpenLM can enforce your deployment and acceptable-use guidelines automatically at the point of checkout.
For example, if a contract limits a tool to a specific role, project, or license pool, OpenLM applies that rule before it grants access, not after someone’s already used a seat they shouldn’t have.
Another important compliance feature that comes with OpenLM is geographical restrictions. Considering the diverse geographical usage scope of all the licenses in your environment, OpenLM flags if there is any discrepancy in local or global license usage.
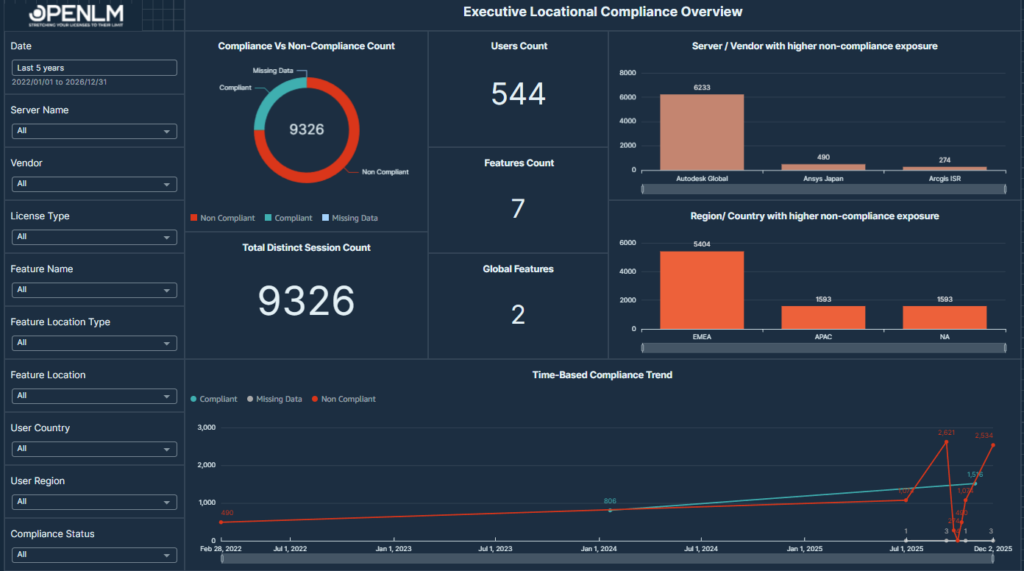
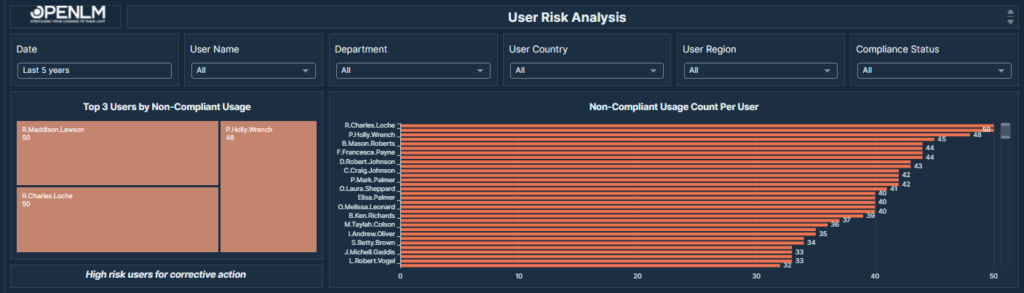
Thus, when a vendor comes to review compliance with their software compliance policy, you already have the answer: who used what, where, and under which rules, all in one audit-ready record.
Frequently asked questions
Is software compliance the same as software asset management?
No. Software asset management is the broader discipline of tracking, managing, and optimizing all software assets across their lifecycle. Compliance is one piece of that discipline, focused specifically on staying within your license terms. You can read more about how the two fit together in the context of ITAM standards like ISO/IEC 19770.
How often should you review your software compliance policy?
Review it at least once a year, and revisit it any time you add a major new software vendor, change your deployment model, or go through a merger or divestiture. Licensing terms change fast, and so does your own usage. Keep the policy moving at that pace, not the calendar’s.
What happens if your organization fails a vendor’s software compliance audit?
Outcomes vary by vendor and severity, but common consequences include a true-up payment covering the overage retroactively, added penalty fees, and a weaker negotiating position at your next renewal. Repeat or serious findings can also push a vendor toward stricter terms or more frequent audits going forward. Failing an audit is rarely just a compliance problem; it’s a budget and negotiating-leverage problem too.
Who should own software compliance inside an organization?
There’s no universal answer, but most organizations do best naming a single owner, often an IT director or software asset manager, even though execution touches procurement, finance, and engineering leads along the way. Shared ownership across several teams often quietly becomes no ownership. Name one person accountable, and let everyone else act as a stakeholder.
Can employees create a compliance problem just by traveling with a licensed laptop?
Yes, more often than most IT teams expect. Some vendors, Autodesk among them, tie certain subscriptions to a home country and cap how long a user can work from elsewhere, often around 90 days in a rolling 12-month period, before a different license type is required. An employee on an extended overseas assignment can drift out of compliance without installing anything new or sharing a seat, simply by staying abroad longer than the license allows.
Does a compliance policy need to address travel or geographic use rights specifically?
If your organization runs specialty engineering or design software with employees who travel or work across borders, yes. A policy that only tracks seat counts and installs will miss this type of gap entirely, since the right person is using the right device, just outside the geography the license terms allow.